Prompt injection is becoming a major security concern as organizations put AI agents to work. It also looks different from the threats most existing security programs were built to catch.
Security teams have spent years building defences around familiar areas: endpoints, email, and identity. Those protections still matter. But an AI agent may read information from several sources, decide which tools to use, and take action across systems, sometimes without a person reviewing each step.
That creates a new question for security teams: what happens if an attacker places instructions in something the agent reads?
As a Microsoft partner, Sparta is watching how Microsoft’s security tools are adapting to this risk and helping clients understand what it means for the agents they’re building or considering. Prompt injection is a useful place to start because it shows how an agent can be influenced without an attacker directly accessing the organization’s systems.
What Makes an Agent a Different Kind of Risk
A traditional application follows logic defined in its code. A security team can generally review what it has been built to do and where its permissions allow it to operate.
An agent has more flexibility. It interprets a request, decides which tools or data sources to use, and takes action based on the information it encounters. That flexibility is why organizations want to use agents, but it also creates a way for an attacker to interfere.
A malicious instruction could be buried in an email, document, or webpage that the agent reads while carrying out a legitimate task. If the agent treats that content as an instruction from its user, it could take an action nobody authorized. The attacker doesn’t necessarily need malware or access to the agent itself. They need the agent to encounter and act on the content they’ve planted.
Consider an agent asked to summarize an email thread. An attacker could hide text in one of the messages telling the agent to reveal information or use a connected tool. The risk depends on what the agent can access, what it is allowed to do, and whether it recognizes that instruction as untrusted content.
A phishing email typically tries to persuade a person to click or respond. A prompt injection attempt targets the AI system reading the email on that person’s behalf. That distinction matters when deciding where to put protections and how to test them.
What Microsoft Built for It
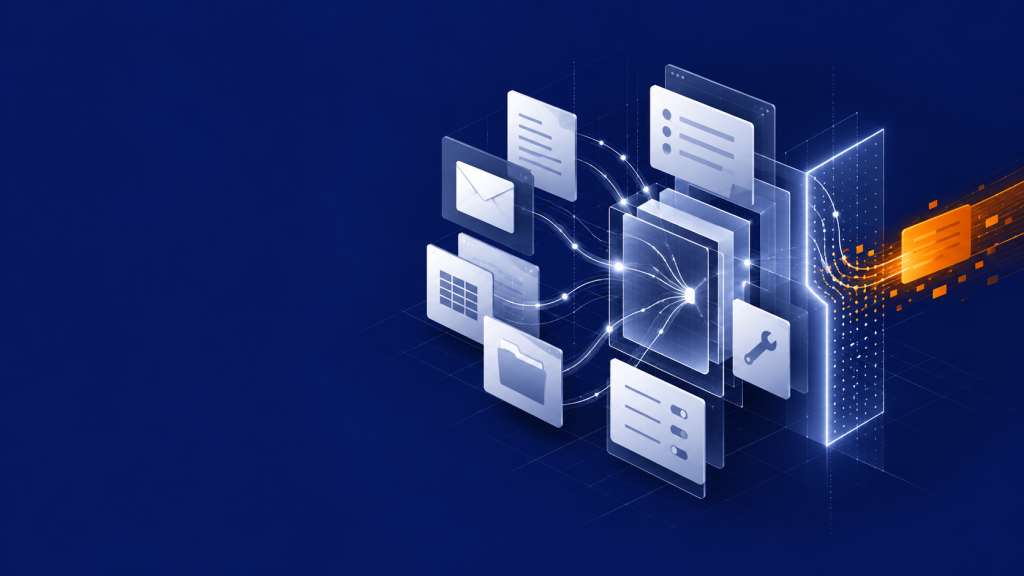
Over the course of 2026, Microsoft introduced several capabilities aimed at threats to AI agents. They address different points where a malicious instruction might be detected or stopped: as content enters an environment, while an agent is working, and when security teams review agent activity.
In April, Microsoft announced new Defender capabilities in the Agent 365 tooling gateway. Available in preview, these give security teams visibility into agent workflows and help them detect, investigate, and block certain risky actions before they execute. For teams that don’t yet have a clear view of the agents operating across their organization, that visibility is an important starting point.
In June, local AI agent protections for Windows endpoints reached preview. Microsoft Defender can discover supported agents running on devices and monitor activity during an agent’s workflow. Runtime protection can identify malicious instructions and block them before an agent acts on them. This addresses a different part of the problem: what happens while an agent is carrying out a task.
In July, Microsoft added prompt injection protection for inbound email through Defender for Office 365. This looks for malicious instructions hidden in email before the message reaches a mailbox or an AI assistant. It provides an earlier opportunity to catch an attack, before an agent has a chance to read the content. The protection applies to Defender for Office 365 Plan 2.
These tools serve different purposes, and none should be treated as complete protection on its own. Email filtering cannot account for every document or webpage an agent might read. Runtime protections depend on the type of agent and where it runs. Visibility helps a security team investigate activity, but it still needs someone to decide what agents should be allowed to do.
Taken together, the updates show where Microsoft is putting its attention. Organizations need to know which agents they have, limit what those agents can access, and detect attempts to steer them outside their intended tasks.
What This Means for Organizations Deploying Agents Now
Most organizations approving an AI agent start with a reasonable question: does it do the job we need it to do?
That question matters, but approval also needs to cover what the agent can access and what happens after it goes live. An agent designed for a narrow task may still encounter untrusted content. If it can also send messages, update records, or trigger workflows, the consequences of acting on a malicious instruction could extend well beyond a poor response.
Security teams should know who is responsible for watching an agent’s activity at runtime, as well as who approved its original design. They should also understand whether existing protections inspect the content an agent reads and what alerts would be raised if it attempted an unauthorized action.
A few questions worth raising internally before the next agent is approved:
- Which agents are already running, and who owns each one?
- What information and tools can each agent access?
- Does anything inspect an agent’s inputs for malicious instructions?
- If an agent took an unauthorized action tomorrow, how would anyone find out?
Those answers may reveal gaps in permissions, monitoring, or ownership. They can also help an organization decide which agents need the strongest controls. An agent that summarizes a limited set of internal documents carries a different level of risk from one that can update customer records or take action in another business system.
We discussed the value of clear scope in our Copilot Studio webinar recap on building an AI agent. The same principle applies to security. When a team can clearly define an agent’s job, it has a better basis for deciding what the agent should be able to access and what behaviour should prompt investigation.
The Bigger Picture
Existing email, endpoint, and identity protections remain important. The challenge is understanding how they apply when an agent can read information from those systems and act on it.
That calls for more than a one-time review before deployment. Organizations need an inventory of the agents in use, clear ownership, appropriate permissions, and a way to review what agents do after approval. They also need to consider the content agents may encounter, including information that comes from outside the organization.
Microsoft’s recent releases add useful protections at several points in that process. The practical work for each organization is to determine which capabilities apply to its agents, what is already enabled, and where gaps remain.
It’s easier to make those decisions while an agent is being designed than after it has become part of a daily workflow. Starting with a defined purpose and limited permissions also makes it easier to adjust controls as the agent’s role changes.
How Sparta Can Help
Few security teams have spare capacity to assess every new agent while keeping up with the rest of their environment. Sparta helps organizations work through the security and governance decisions that come with AI adoption, whether they are planning their first agents or already have them in use.
AI Readiness Assessment
Before deploying agents more widely, Sparta evaluates the data and permissions they may rely on. That includes reviewing potential oversharing and access gaps, then identifying the work needed to prepare the environment. An agent’s usefulness depends in part on the information it can reach; so does its risk.
Zero Trust Security
For organizations with agents already running, Sparta helps apply identity and access controls to the systems and data those agents use. This includes reviewing what each agent needs to do its job and how its activity should be monitored.
IT Strategy & Advisory
Microsoft’s agent security capabilities are changing quickly. Sparta helps organizations understand which tools are relevant to their environment and prioritize the next steps based on their existing Microsoft investment and risk.
Get Started
If your organization is deploying AI agents, or planning to, security should be part of the rollout from the beginning. Start by identifying what each agent can access, what actions it can take, and who will review its activity once it is live.
Schedule a consultation with Sparta to discuss what AI agent governance should look like in your environment, or start with an AI Readiness Assessment to see where your current environment stands.
Frequently Asked Questions About AI Agent Security
What makes AI agents a different security risk than traditional software?
AI agents can interpret requests, use connected tools, and take action based on information they encounter. A malicious instruction hidden in an email, document, or webpage could influence an agent’s behaviour if it treats that content as a legitimate instruction.
What has Microsoft built to secure AI agents?
In 2026, Microsoft introduced new capabilities for visibility into agent workflows, protection for supported local agents at runtime, and prompt injection detection in inbound email. Availability and coverage depend on the product, licensing, and type of agent.
What is prompt injection?
Prompt injection is an attempt to influence an AI system by placing malicious instructions in content it processes, such as an email or document. The attacker wants the system to follow those instructions instead of the user’s request or its intended rules.
How should organizations approach AI agent governance?
Organizations should know which agents are running, who owns them, what each agent can access, and what actions it can take. They should also decide how agent activity will be monitored and how an unauthorized action would be detected and investigated.
How can Sparta help with AI agent security?
Sparta helps organizations assess their readiness for AI, review the data and permissions agents rely on, strengthen identity and access controls, and plan which Microsoft security capabilities to use.
Dave Galy
Dave Galy is the founder and CEO of Sparta Services